Editor's brief
This guide explores modern web development, covering shifts to microservices, essential frontend and backend technologies, API design, cloud deployment, and responsive design. Learn to build dynamic, scalable, secure, and user-centric web applications to thrive in the evolving digital landscape.
#Web Development
#Microservices
#Cloud Computing
#Responsive Design
Alright, tech enthusiasts, gather 'round! If you're anything like me, you're constantly hyped about what's next in the digital arena. Just like the gaming world is always dropping new engines, mind-bending graphics, and innovative gameplay mechanics, the realm of modern web development is a non-stop, electrifying evolution. We're talking about a rapidly changing ecosystem, relentlessly driven by an onslaught of new tools, cutting-edge methodologies, and, most importantly, user expectations that are always pushing the envelope. Stagnation? Not in this game! To truly master this space, you need to be less of a casual player and more of a pro-gamer, always adapting, always learning the latest patch notes. This comprehensive guide will navigate you through the essential technologies and best practices for building dynamic and scalable web applications, ensuring your creations are ready for the demands of today's digital users. The Evolving Landscape of Modern Web Development Monoliths, microservices, and serverless services are architectural choices rather than a universal sequence of upgrades. Microservices can support independent deployment and scaling, but introduce distributed-system concerns such as service discovery, data consistency, and more complex testing. A well-structured monolith can be appropriate for a smaller system or team. [1] Serverless services shift infrastructure tasks to a provider, while application design, configuration, security, and operating limits sti...
Alright, tech enthusiasts, gather 'round! If you're anything like me, you're constantly hyped about what's next in the digital arena. Just like the gaming world is always dropping new engines, mind-bending graphics, and innovative gameplay mechanics, the realm of modern web development is a non-stop, electrifying evolution. We're talking about a rapidly changing ecosystem, relentlessly driven by an onslaught of new tools, cutting-edge methodologies, and, most importantly, user expectations that are always pushing the envelope. Stagnation? Not in this game! To truly master this space, you need to be less of a casual player and more of a pro-gamer, always adapting, always learning the latest patch notes. This comprehensive guide will navigate you through the essential technologies and best practices for building dynamic and scalable web applications, ensuring your creations are ready for the demands of today's digital users.
The Evolving Landscape of Modern Web Development
Monoliths, microservices, and serverless services are architectural choices rather than a universal sequence of upgrades. Microservices can support independent deployment and scaling, but introduce distributed-system concerns such as service discovery, data consistency, and more complex testing. A well-structured monolith can be appropriate for a smaller system or team. [1] Serverless services shift infrastructure tasks to a provider, while application design, configuration, security, and operating limits still need attention. [2]
Some applications benefit from live updates, such as chat or collaborative tools; others work well with ordinary request-response interactions. WebSockets provide an established connection for sending and receiving data between a browser and server. [3] Choose a communication method for the actual interaction requirements rather than assuming every site needs constant real-time traffic.
Iterative development can help teams respond to feedback. The Agile Manifesto principles emphasize frequent delivery of useful software, collaboration, and adaptation to changing requirements. [4] These principles guide a process; they do not guarantee that a particular release is secure, stable, or useful. Short feedback loops work best when paired with appropriate review and validation.
Security belongs in design, implementation, and operation. Input validation alone does not prevent SQL injection or cross-site scripting. Use parameterized database queries and context-appropriate output encoding or sanitization, alongside other controls. [5] [6] Authorization must be checked on the server for the requested action and resource. [7] An API-first process can help document decisions, but does not make a system secure by itself.
Developer tools can shorten feedback loops through repeatable builds, version control, testing, and deployment automation. Their value depends on how well they fit the project and team. A productive environment supports careful work, but adding more tools does not automatically improve software quality or delivery speed.
Leveraging Frontend Frameworks for Rich User Interfaces
React, Angular, and Vue are examples of tools for building interactive interfaces, while simpler pages may need little or no client-side framework. Select an approach based on interaction requirements, accessibility, performance, maintenance, and team experience. No framework is indispensable for every website.
A component-based architecture organizes interfaces into reusable units, such as buttons, forms, or navigation. React's documentation describes components as UI building blocks. [8] Reuse can make changes easier, but shared components still need stable interfaces and testing: changing one component can affect many screens rather than automatically fixing every instance safely.
Choose state management patterns for the scope of the data. Local state may be sufficient, while shared state can require explicit ownership and coordination. For new Vue applications, the official guide recommends Pinia; Vuex remains in maintenance mode. [9] A client-side store does not automatically synchronize different users, replace a database, or resolve server-side concurrency.
The declarative nature of tools such as React changes how developers express an interface. Instead of specifying every DOM operation and how to perform it, they describe what the UI should look like for the current state. [10] The framework updates the interface, but the abstraction does not guarantee the most efficient possible rendering for every application.
Use performance optimization techniques where measurements show a benefit. Code splitting can defer loading parts of an interface; React's lazy API, for example, defers a component's code until it is first rendered. [11] Extra loading boundaries also need suitable loading states and error handling. Splitting every component is not automatically faster.
Project build tools can provide a development server and a production asset pipeline. Vite's current guide describes its development server and a production build using Rolldown. [12] Browser compatibility, asset processing, and optimizations depend on the configuration and plugins; a successful build alone does not prove that every target browser works correctly.
accessibility (a11y) standards must be baked into the design and implementation of frontend components from the start. WCAG 2.2 addresses requirements including keyboard operation, contrast, labels, and programmatically available names and relationships. [13] Semantic HTML and accessible interaction patterns need testing in context; a component framework does not establish conformance automatically.
Building Robust Backends with Scalable Technologies
Alright, fellow tech enthusiasts, let's dive deep into the very core of what makes our favorite online experiences tick: the backend! In the exhilarating world of modern web development, a robust backend isn't just a nice-to-have; it's the fortified castle keeping our entire application secure, performant, and ready for prime time. Just like a meticulously designed game engine, the backend handles the heavy lifting – business logic, data storage, and the all-important user authentication – ensuring a smooth, reliable experience for everyone. If you're serious about building dynamic and scalable web applications, mastering these backend technologies is non-negotiable.
Select backend technologies according to the workload. Node.js uses an event loop and worker pool for different operations, so blocking either can delay other work. [14] It can suit I/O-heavy applications, but high concurrency is not guaranteed: CPU-heavy code, slow dependencies, and resource limits still require design and measurement.
Python and Java provide other options. Django includes facilities such as an object-relational mapper and administration interface. [15] Flask is a lightweight WSGI framework that can support applications of different sizes. [16] Spring Boot helps create stand-alone Spring applications and supplies production-oriented features such as metrics and health checks. [17] These features do not make any stack inherently more reliable or scalable than a properly designed alternative.
Database selection should follow query patterns, consistency needs, transactions, operational requirements, and the data model. PostgreSQL supports transactions that group operations into an all-or-nothing unit. [18] MongoDB supports flexible document structures, but still requires deliberate data modeling. [19] Cassandra uses a distributed design with replication and consistency trade-offs. [20] The SQL or NoSQL label alone does not establish suitability or performance.
Design authentication and authorization mechanisms separately: identifying a requester does not establish what they may do. Check permissions for each protected action and resource, applying least privilege. [7] If using JWTs, validate the signature and relevant claims, including the expected issuer and audience, under an explicit token profile. The format alone does not establish trust or eliminate revocation and session-management decisions. [21]
Capacity planning includes load balancing strategies, application resource limits, and the capacity of databases and other dependencies. Independent services may scale separately, but distributed systems introduce additional failure modes. [1] Autoscaling has quotas and response limits; it does not guarantee uninterrupted service during a traffic surge. Test realistic workloads and failure scenarios rather than relying on a platform label. [2]
Mastering API Design for Seamless Communication
Alright, fellow tech adventurers! In the fast-paced arena of modern web development, where applications are more interconnected than ever, there's one unsung hero that truly dictates the flow of information: the Application Programming Interface, or API. Think of it like the intricate network protocol that allows your favorite online game client to talk to the server, fetching player data, sending commands, and updating the leaderboard in real-time. Without a well-designed API, our frontend UIs would be lonely islands, our backend logic a silent monolith, and third-party integrations a non-starter. Effective API design isn't just a technical detail; it's the cornerstone of communication, the very backbone that ensures seamless interaction across all parts of your web application, from the dazzling UI to the robust database, and even extending to external services. It’s about creating a language that all your digital components can speak fluently, ensuring that data flows as smoothly as a perfectly executed combo in an esports match.
RESTful APIs apply an architectural style with constraints including stateless interactions and a uniform interface; using JSON over HTTP does not by itself satisfy REST. [22] Under HTTP semantics, GET retrieves a representation, POST requests resource-specific processing, PUT creates or replaces the target resource's state, and DELETE removes its association with current functionality. [23] Application-specific actions still need clear contracts.
GraphQL provides a schema and query language that let clients select fields for a response. [24] This can reduce unwanted data transfer for some interfaces, but REST APIs can also offer tailored representations. Query complexity, resolver behavior, authorization, and caching determine practical efficiency; GraphQL does not guarantee faster execution or simpler operations.
When versioning APIs, plan how consumers will handle changes and when old behavior will be retired. A path such as /api/v1/users is one option, while other strategies use headers or query parameters. [25] Version numbers do not automatically maintain compatibility: document breaking changes, provide migration guidance, and test the promises made to existing clients.
Provide clear and comprehensive API documentation covering requests, responses, errors, and authentication requirements. OpenAPI is a specification for describing HTTP APIs; Swagger is also the name of a tooling ecosystem and should not be treated as an interchangeable name for every OpenAPI tool. Descriptions can support documentation and code-generation workflows, but must remain aligned with actual behavior. [26]
OAuth 2.0, JWTs, and API keys serve different security roles. OAuth 2.0 concerns delegated authorization, with current security guidance provided by RFC 9700. [27] JWT is a claims format that must be validated for its intended purpose; signing does not inherently encrypt its contents. [21] API keys can identify calling applications, but should not be the sole protection for sensitive resources. None of these mechanisms replaces endpoint authorization. [28]
Use rate limiting and throttling to control resource consumption under a defined policy. Implementations may reject excess requests or delay work, and terminology varies. OWASP recommends returning HTTP 429 for requests arriving too quickly. [28] Limits are one protection against abuse, rather than a complete defense against distributed denial-of-service attacks.
WebSockets provide real-time, bidirectional communication through an established connection. [3] They can suit chat and live feeds, but do not guarantee latency or delivery semantics by themselves. Plan authentication, reconnect behavior, message limits, and slow-consumer handling, and consider whether simpler polling or server-sent updates meet the requirement.
Strategic Cloud Deployment and Infrastructure Management
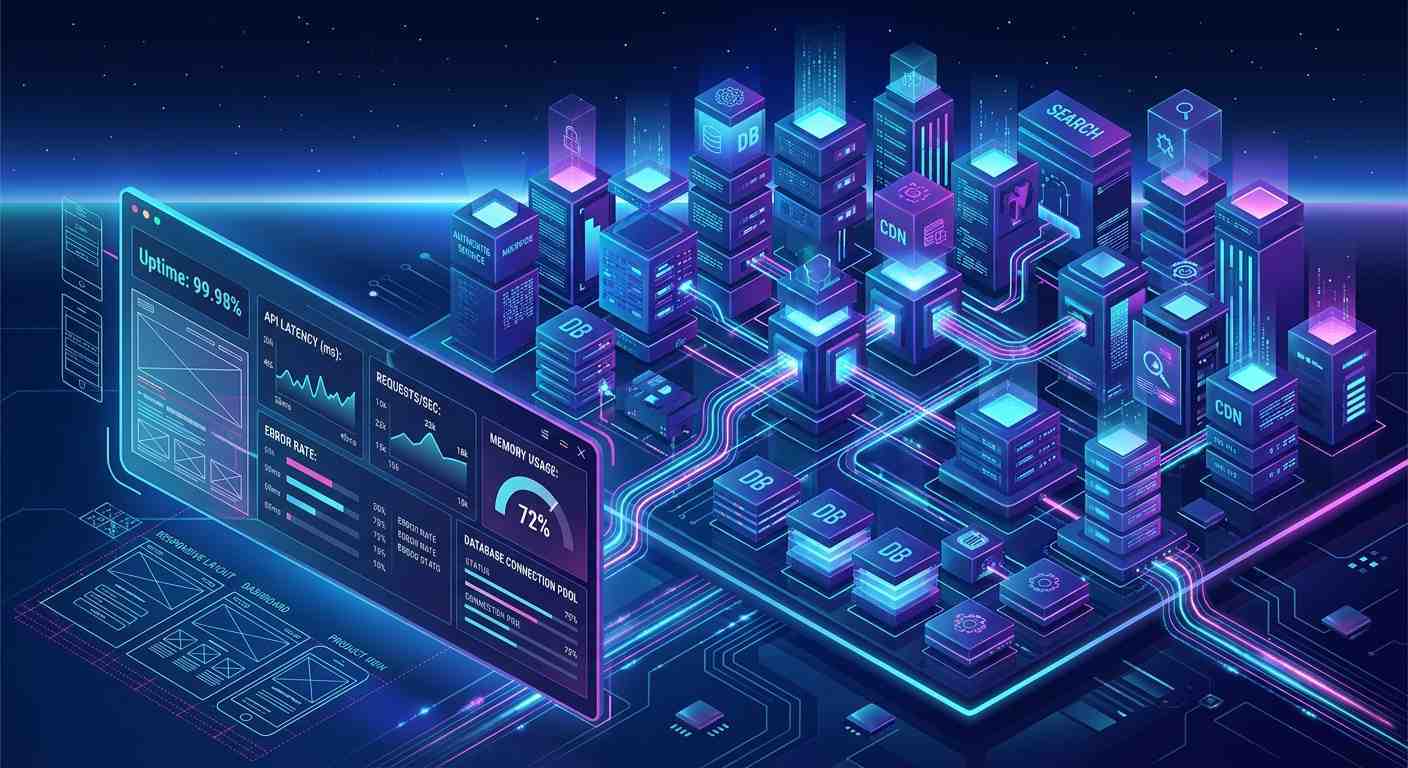
Strategic Cloud Deployment and Infrastructure Management connects application code with a service people can use. Deployment choices should account for expected demand, availability goals, security, cost, and the team's ability to operate the system. A cloud provider offers capabilities, while the application still needs configuration and validation.
Cloud deployment platforms like AWS, Azure, and Google Cloud offer infrastructure for hosting web applications. Select services and scaling policies for the workload rather than assuming resources expand without limit. For example, AWS Lambda scaling is constrained by concurrency limits. [2] Budgeting and reliability planning must include dependencies and failure behavior as well as compute capacity.
Containerization with Docker and orchestration with Kubernetes can support deployment and scaling. Containers package an application with required runtime dependencies, while still depending on the host environment and configuration. [29] Kubernetes manages containerized workloads and supports mechanisms such as rollouts and self-healing. It does not build the application or remove the need for operational decisions. [30] Running an image locally therefore does not guarantee identical production behavior.
Continuous integration and deployment pipelines can automate build, test, and release steps. Tools such as GitHub Actions run workflows in response to configured events. [31] Continuous delivery can retain a manual release decision, while continuous deployment automates release after the configured gates pass. Tests and gates cover selected risks; they do not guarantee that a change is bug-free or require every successful commit to reach production.
Serverless computing shifts server operation tasks to a provider. Event-driven functions can be useful for suitable workloads, but developers still manage code, configuration, permissions, dependencies, and failure handling. AWS Lambda automatically scales function execution environments within its limits. [2] Evaluate latency, quotas, and the full cost model rather than assuming serverless is always cheaper or unlimited.
Infrastructure as Code can make infrastructure changes reviewable and repeatable. Terraform describes resources in configuration files and uses a plan-and-apply workflow to manage changes. [32] Environments can intentionally differ, and external changes or provider behavior can cause drift. Version-controlled definitions reduce some manual work, but do not guarantee identical environments or safe changes without review.
Monitoring and logging help teams understand application behavior and investigate problems. Observability draws on signals such as metrics, logs, and traces. [33] Choose useful instrumentation, alerts, and response procedures, while protecting sensitive information in telemetry. Collecting signals does not itself prevent outages or ensure someone can act on them.
Achieving Universal Accessibility Through Responsive Design: It's Not Just a Trend, It's the Game Changer!
Responsive design helps layouts adapt to different viewports. It is an important part of reaching every single user as an aspiration, but does not establish universal accessibility. Keyboard access, understandable content, accessible controls, and compatibility with assistive technology require separate attention. [13]
A mobile-first approach can begin with a simple layout and add adaptations for wider viewports. It encourages prioritization, but you do not have to start with the smallest imaginable screen or assume the result is automatically faster. Choose breakpoints and layouts around the content and intended interactions. [34]
Combine fluid grids, flexible images, and media queries to adapt layouts. Grid units such as fr distribute available space, while viewport units such as vw/vh relate to viewport dimensions. Image styles including max-width: 100%; and height: auto; can constrain an image while preserving its proportions. [34] Check intrinsic sizing and overflow; relative units alone do not prevent layout problems.
Keep prioritizing content and functionality as layouts change. Reordering or collapsing content should preserve a logical reading and focus order. Do not remove essential information merely because the viewport is narrow. Test menus, forms, and error messages as part of the complete task, rather than judging a layout by a static screenshot. [13]
Touch-friendly interfaces and appropriate input handling support mobile use. WCAG 2.2 success criterion 2.5.8 sets a Level AA pointer-target requirement of at least 24 by 24 CSS pixels, with specified exceptions including spacing. [35] This is different from a universal 48-pixel rule. Larger targets can be helpful, and interfaces should also accommodate keyboard and other available input methods.
Performance considerations, such as optimized image loading and efficient CSS, matter for mobile experiences. Size and compress images appropriately, then measure actual loading and interaction behavior. Browser image lazy loading can defer offscreen images, but above-the-fold images and likely largest-contentful-paint images generally should not be lazy loaded. [36] Optimization choices depend on the page and devices being served.
Testing across representative devices and browsers helps identify inconsistent behavior. Browser tools can simulate viewport sizes and some conditions, but cannot reproduce every property of real physical devices. Chrome's documentation describes Device Mode as an approximation of the experience. [37] Include relevant browsers, touch and keyboard tasks, and assistive technology in the test plan.
Responsive design works alongside accessibility, performance, and usability work. The aim is to help everyone complete the intended task, while recognizing that conformance and usability require evidence from the actual interface. Flexible layouts alone cannot guarantee inclusion or future compatibility.
Conclusion
Modern web development combines architecture, interfaces, data, APIs, deployment, and ongoing operation. Each choice has trade-offs: microservices, frameworks, tokens, and cloud services solve particular problems rather than guarantee quality. Start with user needs, consult current documentation, and validate security, accessibility, performance, and reliability in the resulting application.
Greetings! Daniel Kim here. I’ve spent 4 years navigating the world of gaming and tech columnist who tracks esports, game design trends, and the communities that form around them., and my roots in South Korea and training in Game Design continue to shape how I tell stories and break down ideas.